Protecting Your Business from AI-Generated Phishing Attacks: Advanced Techniques
Part 2 of our Phishing Protection Series
This article builds on the fundamentals covered in Part 1. If you haven’t read it yet, start here:
👉 Read Part 1: Phishing Protection
In today’s digital landscape, phishing attacks have become increasingly sophisticated, mainly caused by the rise of AI-generated content. As these attacks continue to evolve, businesses need to stay ahead of the threats and implement effective solutions to prevent them. In this article, we will discuss the importance of custom model development for fraud and phishing detection, as well as alternative AI solutions for phishing prevention training.
The Rise of AI-Generated Phishing Attacks
Phishing attacks have long been a significant threat to businesses, but the emergence of AI-generated content has elevated them to a new level. Deepfake phishing scams utilise AI-generated audio or video to deceive victims into divulging sensitive information and are becoming increasingly prevalent. Additionally, AI-powered Gmail phishing attacks designed to mimic those from legitimate senders are also on the rise.
These attacks can be particularly effective in targeting businesses and individuals, as they often appear to originate from trusted sources. A 2024 IBM study revealed that 70% of surveyed businesses have fallen victim to a phishing attack, with the average cost per attack at $4.88 million.
The use of AI-generated content in phishing attacks makes them even more challenging to detect, as they can be designed to mimic the tone, style, and language of legitimate communications. This is where custom model development for fraud and phishing detection can be beneficial.
Custom Model Development for Fraud and Phishing Detection
Custom model development for fraud and phishing detection involves creating a machine learning model specifically designed to detect and prevent phishing attacks. The dataset used for model training consists of known phishing attacks and legitimate communications to recognize the patterns and characteristics of phishing threats.
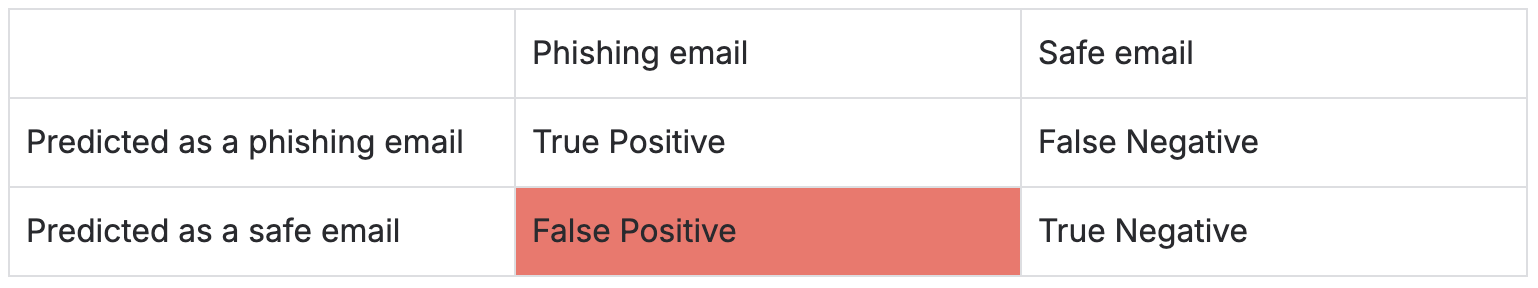
The benefits of custom model development for businesses include improved detection rates and reduced false positives. By creating a model trained to your business’s specific needs, you can enhance the accuracy of your phishing detection and minimise the risk of false positives.
The process of developing a custom model has several steps: data collection, data preparation, model training, and model evaluation. This involves collecting a dataset of known phishing attacks and legitimate communications, and then training the model on this data to learn the patterns and characteristics of phishing attacks.
Once the model is trained, it can be continuously updated and maintained to stay ahead of evolving threats. This means regularly updating the model with new data and retraining it to ensure its continued effectiveness.
Using Open-Source AI for Phishing Detection
Recently, Large Language Models (LLMs) have been used for phishing email detection through their ability to recognise patterns. We advise using an open-source internally hosted model. This way, the internal business communications are not exposed to unnecessary vendor risks. Next, we will present two ways to achieve this.
The first, performance-limited but easy to implement approach, is integration of a specialised model for phishing detection from a known repository such as Hugging Face. A prominent example is PhishSense-1B, which has achieved an accuracy of 0.975 and a precision of 0.958. The open-source model can be hosted on local infrastructure – either using existing hardware or a company-controlled cloud.
For optimal performance, we recommend using a fine-tuned model. Ideally, it must be trained on a carefully curated dataset with company-specific examples comprising a balanced mix of phishing emails and legitimate, safe emails.
This proactive approach serves as a vital precaution against phishing attacks, allowing the model to develop a more nuanced understanding of the subtleties that distinguish malicious from harmless communications. To achieve this, we suggest starting with an existing open-source model that possesses a broad understanding of the English language, and then further fine-tuning it with targeted phishing email data to enhance its detection capabilities.
AI-Powered Phishing Protection Software
AI-powered phishing protection software is designed to detect and prevent phishing attacks in real-time. These software solutions use machine learning algorithms to analyse incoming emails and identify potential phishing attacks.
The features and capabilities of these software solutions include AI-driven phishing simulation platforms, which simulate phishing attacks to test employee awareness and response. They also include an AI-driven protection mechanism that blocks access to known phishing websites and prevents employees from accessing them.
Integrating these solutions with existing cybersecurity measures is essential to ensure their effectiveness. This involves integrating the software with existing email security solutions, such as spam filters and antivirus software, to ensure that all incoming emails are scanned for phishing threats.
AI-Powered Phishing Training Modules
Employee training is a vital component of any phishing prevention strategy. AI-powered phishing training modules educate employees on the risks of phishing attacks, empowering them to identify and prevent these threats. By leveraging these modules, organisations can enhance employee awareness and significantly reduce the risk of phishing attacks, ultimately strengthening their overall security posture.
Conclusion
In conclusion, protecting your business from AI-generated phishing attacks requires a comprehensive AI-powered protection approach. This includes custom model development, custom phishing training modules, and phishing protection software. Another possibility is to use open-source LLMs for phishing anomaly detection, which can be hosted as is or fine-tuned on proprietary data for extra performance. By implementing a set of these solutions, you can stay ahead of threats and protect your business from the risks of phishing attacks.
Frequently Asked Questions (FAQs)
Q1: How to train employees to identify AI-generated phishing?
AI-powered phishing training modules can be used to educate employees on the risks of phishing attacks, empowering them to identify and prevent these threats.
Q2: How can AI be used in phishing attacks?
AI can be used in phishing attacks to generate content that mimics legitimate communications, making it challenging to detect. AI-powered phishing attacks can also use deepfake technology to deceive victims.
Q3: Why do phishing emails generated by AI seem so real?
AI-generated phishing emails can be designed to mimic the tone, style, and language of legitimate communications, making them appear more convincing and real.
Q4: How to identify AI-generated phishing emails?
Unlike traditional phishing emails, the AI-generated ones are usually grammatically correct. But, they still have induced urgency and links as a way to catch a victim. A distinct characteristic of AI-generated phishing emails is unnatural monotonic tone.
Q5: How to stop AI-generated phishing attacks?
Educate employees on how to identify and report suspicious emails, and consider implementing user behaviour analytics to detect anomalies in user behaviour. Additionally, use two-factor authentication and implement anti-phishing measures such as sender policy framework (SPF), domain keys, and DMARC to prevent phishing emails from reaching users’ inboxes. Additionally, AI-powered phishing protection software can help identify threats through anomaly detection approaches.
Q6: How can open-source AI models be used to reduce phishing attacks?
Open-source AI models, such as PhishSense-1B, can be used to detect phishing attacks. Ideally, these should be hosted on internal infrastructure to avoid exposure of private internal communications.
Q7: How does fine-tuning increase the precision of LLMs for phishing detection?
Fine-tuning an open-source LLM on a business’s proprietary data allows it to develop a more nuanced understanding of the subtleties that distinguish malicious from harmless communications, increasing its precision for phishing detection.
Related Services
Open-Source AI